Dieser Artikel ist derzeit nur auf Englisch verfügbar.
GDPR-Compliant Software Outsourcing: A Practical Checklist
The Risk of Data Breaches
For businesses handling European citizen data, data privacy is a legal imperative. When sending code or data offshore, you must ensure you are working with a GDPR compliant software outsourcing partner to avoid catastrophic fines and reputational damage.
The GDPR Compliance Checklist
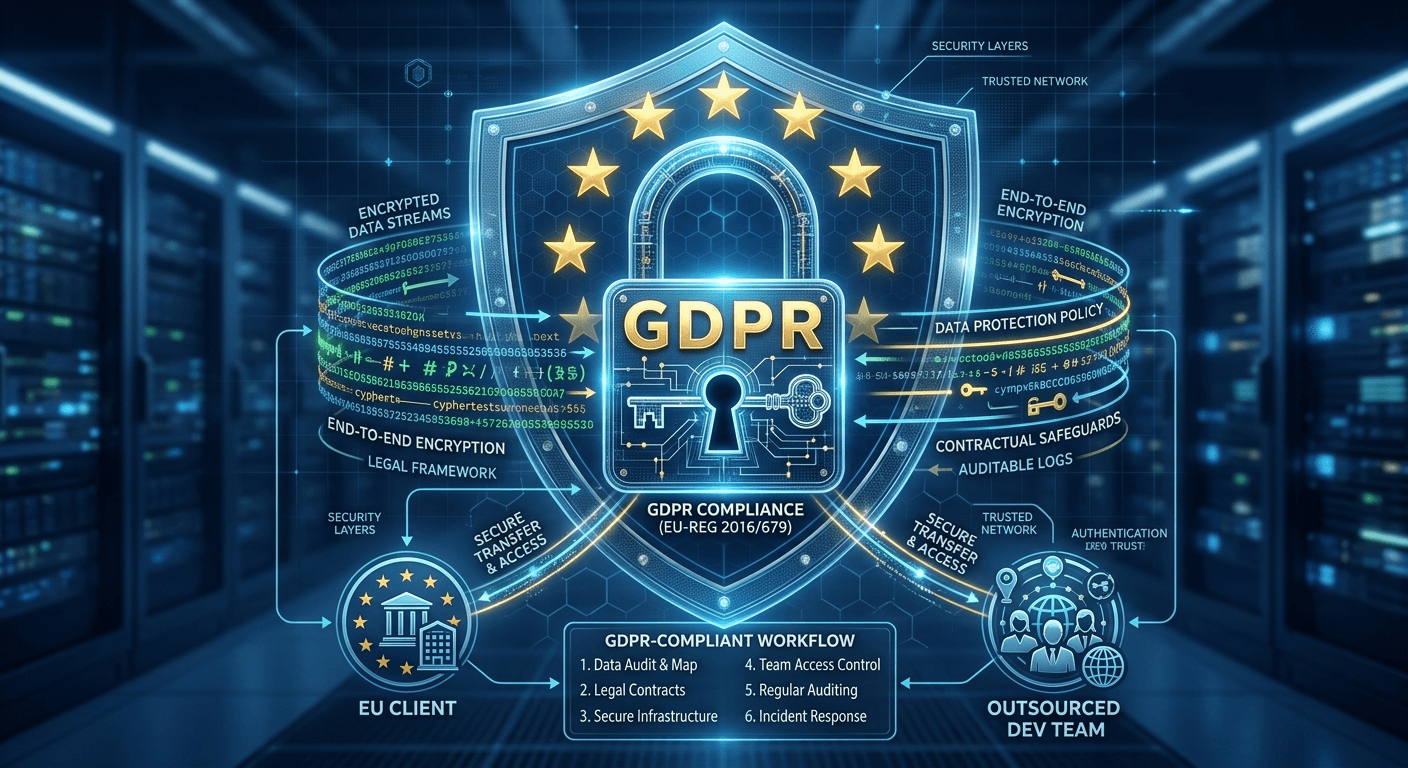
Before signing an agreement, verify that your GDPR compliant software outsourcing partner implements the following:
- Data Processing Agreement (DPA): A legally binding document outlining exactly how they will handle, store, and protect your data as a Data Processor.
- End-to-End Encryption: Strict protocols for data encryption both in transit (TLS) and at rest (AES-256).
- Access Controls: Implementation of Zero Trust architecture, Multi-Factor Authentication (MFA), and strict Role-Based Access Control (RBAC) to limit data exposure.
- Anonymization in QA: Ensuring that production data containing PII (Personally Identifiable Information) is never used in staging or testing environments without proper masking.
Mickiesoft takes data sovereignty seriously. We build highly secure, enterprise-grade architectures that strictly adhere to GDPR and international data protection standards.
Ready to accelerate your project?
Contact Mickiesoft today for a free technical consultation.
Contact UsHäufig gestellte Fragen
Hier finden Sie Antworten auf häufige Fragen zu unseren Leistungen, unserem Vorgehen und unseren Kompetenzen.